

Greek opposition parties have demanded immediate answers from the government after the personal phone number and email address of Prime Minister Kyriakos Mitsotakis were exposed on online data platforms.
The security breach was revealed on September 20 in a front-page investigative report by the Athens Sunday newspaper To Vima tis Kyriakis, written by journalist Niki Lymperaki. The report disclosed that contact details for cabinet ministers, government officials, military personnel, and security officers are accessible on commercial subscription platforms without effective filters or protection.
To Vima tis Kyriakis is a leading national Sunday newspaper in Greece. Kyriakos Mitsotakis has served as Prime Minister of Greece since 2019, leading the ruling New Democracy party.
The investigation highlights the widespread collection and commercial sale of sensitive personal information. The newspaper report noted that mobile numbers, email addresses, and staff databases belonging to ministries, government agencies, and private companies can be located and purchased online. It warned that no real protection exists to safeguard high-ranking political and state officials from digital exposure.
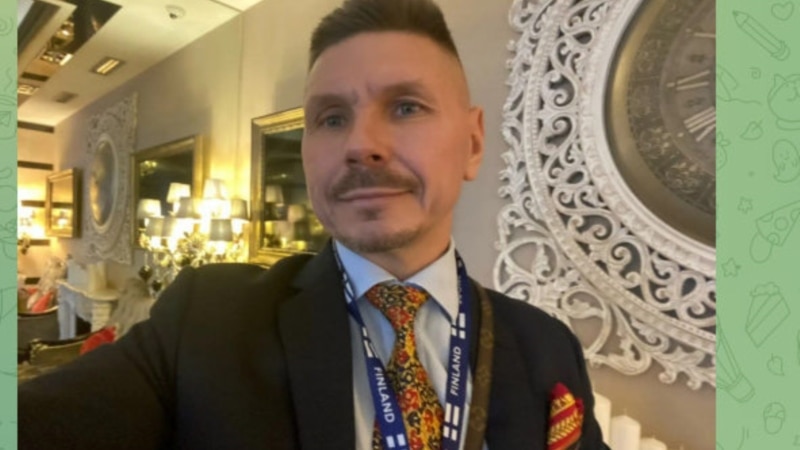
The investigation was prompted when Lymperaki contacted Italian cybersecurity expert Andrea Mavilla, who demonstrated that contact details for prominent Greek figures could be retrieved online within seconds. Mavilla presented records matching Mitsotakis, confirming he possessed the Prime Minister's personal mobile phone number, along with data for ministers, business leaders, banking executives, military officers, and security personnel.
Mavilla noted that while some records in the commercial databases were accurate, others were outdated or incorrect, illustrating that commercial data brokers do not always maintain reliable files. He added that he had repeatedly attempted to notify Greek authorities about the security vulnerability, but received no response, while some officials blocked his communications. Mavilla suggested that officials may have assumed his warnings were a prank or feared an attempted spyware attack.

Government Cybersecurity Response
Michalis Bletsas, commander of Greece's National Cybersecurity Authority, confirmed to To Vima tis Kyriakis that he had received a message from Mavilla regarding the data exposure. Bletsas stated that such details are easily located on the internet without requiring specialized tools or technical expertise.
Bletsas explained that daily digital activities leave constant trails online, with some details posted publicly on social media platforms by users themselves and others leaked when hackers breach corporate databases. He added that data brokers operate in a legal gray zone by aggregating information through various legal and less legal means and selling access to anyone willing to pay.
The National Cybersecurity Authority is the state agency responsible for overseeing digital defense, vulnerability management, and infrastructure security across Greek public administration.
The report warned that possessing direct phone numbers or email addresses of state officials increases vulnerability to phishing campaigns, social engineering, identity theft, address spoofing, and targeted cyberattacks. Security experts noted particular danger if unauthorized actors use an official's credentials to issue fraudulent directives or deceive state agencies and colleagues.
The investigation also examined corporate brokers managing databases containing records on hundreds of millions of individuals worldwide. One data vendor claimed its activities relied on legitimate interest under the European Union General Data Protection Regulation, known as GDPR, for marketing, sales, and executive recruitment. However, the report questioned whether GDPR standards adequately protect European citizens from malicious data exploitation in practice.
The newspaper detailed how contact information is harvested, noting that phone numbers can be gathered when smartphone users grant applications access to their contact directories. Through contact synchronization, personal details of individuals who never granted consent can end up in commercial databases.

Opposition Demands for Accountability
The Panhellenic Socialist Movement, known as PASOK, issued a statement calling on the government and relevant services to state publicly whether they were aware of the data exposure affecting the Prime Minister and cabinet members. PASOK highlighted that sensitive personal records of top leaders were being traded on subscription platforms, noting that the Hellenic Data Protection Authority had already raised national security concerns over data leaks.
PASOK is Greece's primary centre-left opposition party. In its statement, the party recalled a recent security incident involving Secretary General of National Security Thanos Dokos, who shared confidential information regarding the head of the National Intelligence Service, known as EYP, with Russian pranksters who had contacted him via email.
PASOK submitted a series of direct questions to the government, asking what security protocols govern official communications, whether authorities knew that executive contact details were circulating on commercial platforms, and what concrete measures have been taken to contain the leak.

Calls for Institutional Governance
The Digital Policy sector of ELAS issued a separate statement emphasizing that the front-page report reveals a serious issue extending beyond privacy to cybersecurity and potential national security risks. The party statement warned that mass aggregation and cross-referencing of phone numbers, email addresses, and personal details of key public figures creates opportunities for targeted electronic fraud, impersonation, and cyberattacks.
The ELAS Digital Policy sector noted that many data broker platforms operate outside European Union jurisdiction, complicating regulatory enforcement. The announcement stressed that state data sovereignty requires knowing who collects citizen information, from what sources, where servers are located, and under whose legal authority records are stored and processed.
ELAS formulated four specific questions for the government, asking what visibility authorities possess regarding the collection, origin, movement, and commercial sale of Greek citizens' data, and how European privacy laws are enforced in practice. The party inquired whether a systematic mechanism exists to detect data exposure of public figures, what protocols activate upon discovery, and what specific steps were taken after Mavilla notified officials.
The ELAS Digital Policy sector concluded that acknowledging data is easily available online cannot end official inquiry, arguing that public digital resilience requires proactive prevention, systematic exposure detection, and immediate institutional response.